 Deutsch
 English
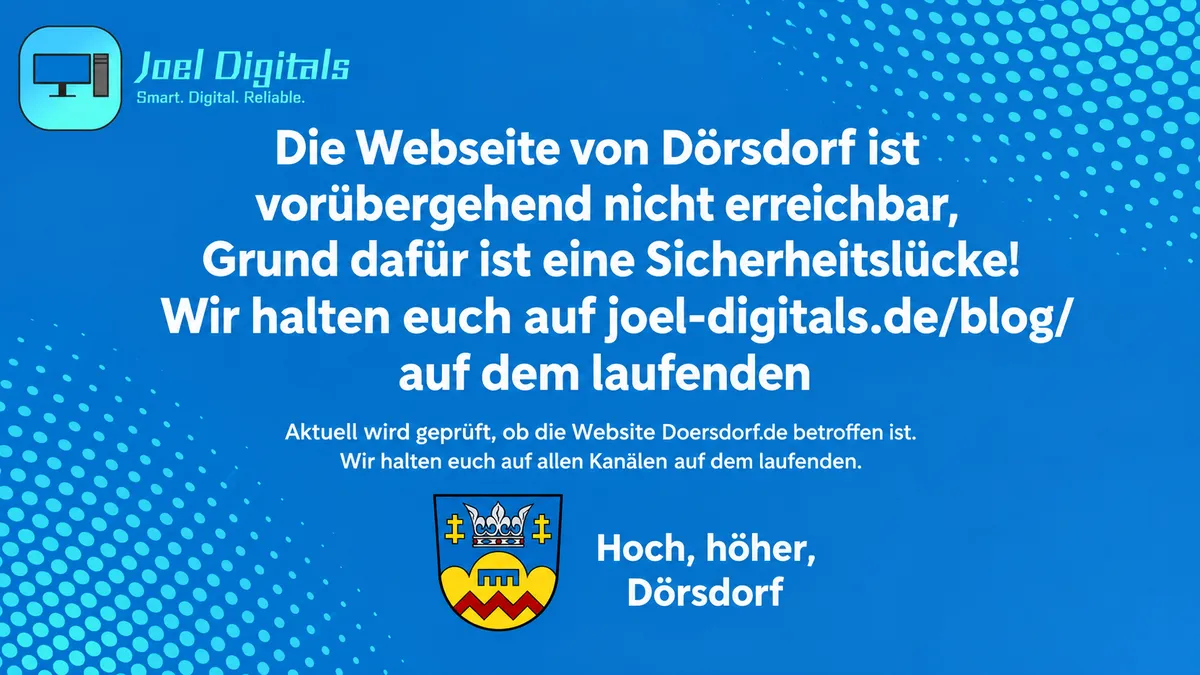
On 21 October 2026, two critical security vulnerabilities in PHP were disclosed ("php2shell", CVE-2026-109618 and CVE-2026-109619). They allow attackers to run their own code remotely on affected servers. The flaw is in PHP itself, so every website running on it is affected, including WordPress sites. Updating WordPress or plugins does not protect against it.
What we did
We immediately checked the websites we manage. The website doersdorf.de runs on PHP 8.1 at the hosting provider STRATO. There is currently no confirmed fix for this version. We have therefore taken the site offline temporarily as a precaution.
We found no signs of a successful attack. Taking the site offline is purely a precaution to protect the website and its visitors.
Live ticker
We keep you up to date on the current status here:
Open the live ticker in a new window
What happens next?
As soon as PHP is updated to a fixed version (8.2.35, 8.3.36, 8.4.27 or 8.5.12), we will bring the website back online. Thank you for your understanding!
Do you run a PHP or WordPress site yourself? Check your PHP version with your hosting provider. We are happy to help if you have questions.
Read next
Comments
Log in to write a comment.
No comments yet. Be the first!